Research Maps Splunk SIEM to MITRE ATT&CK for Ransomware Defense
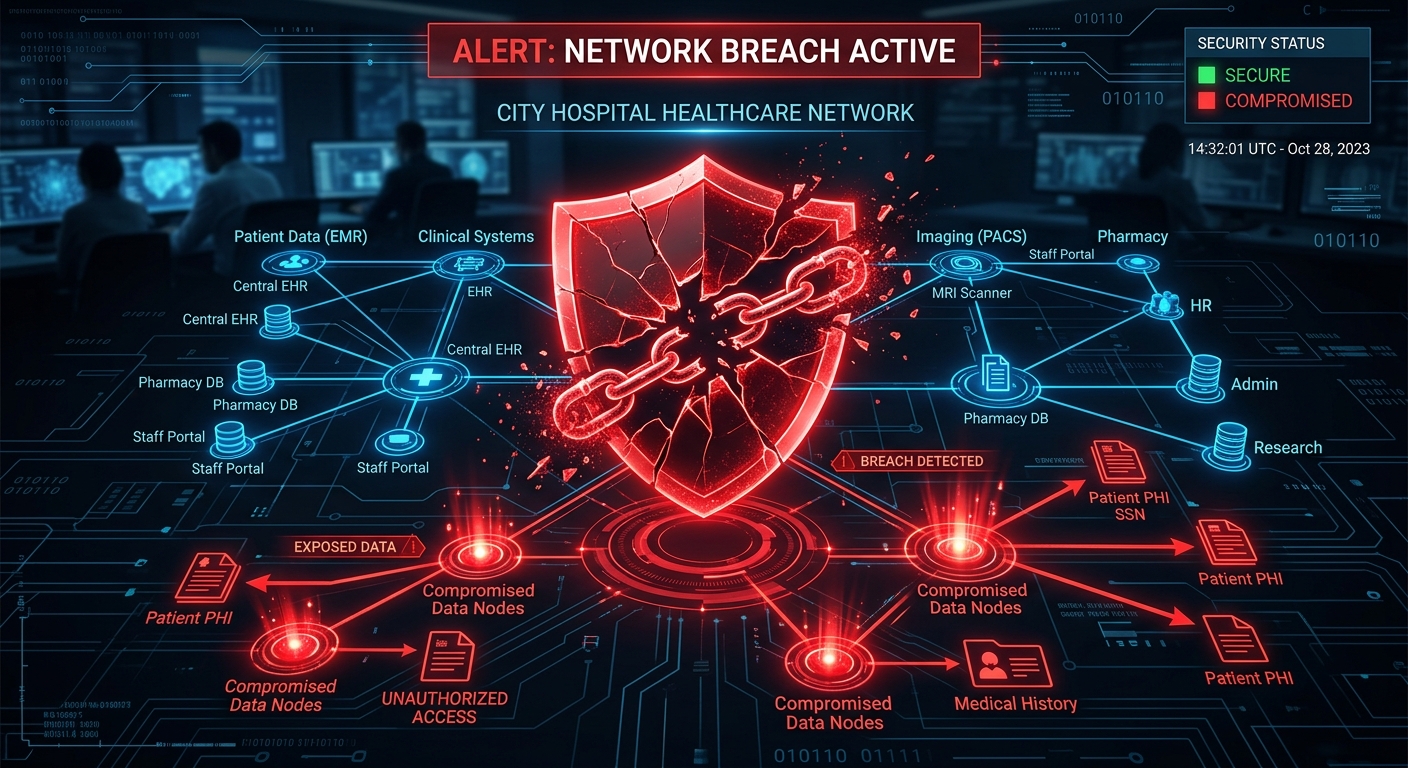
Key Takeaways: Integrating the Splunk Enterprise Security Information and Event Management platform with the MITRE ATT&CK framework gives security teams a more behavior-focused way to detect ransomware. Rather than treating ransomware as a single malware event, the approach maps Splunk analytics to the techniques