 ⬇️
Key Takeaways
- AI-agent adoption is advancing faster than many organizations’ ability to inventory, authorize, monitor and revoke agent access.
- Identity verification alone does not establish whether an agent’s current actions match its authorized purpose.
- Radware’s new Agent Trust Management offering focuses on declared intent, session-level visibility and workflow-specific permissions.
- Effective agent security will require runtime controls alongside identity, API security, logging and established governance practices.
Enterprises are confronting a difficult tradeoff in digital channels: AI agents can act as customers, partners and employees’ automated delegates, but treating every agent request as trusted can expose applications, data and transactional workflows. Blocking automated traffic wholesale is equally problematic when agents are researching products, making bookings or performing authorized business tasks.
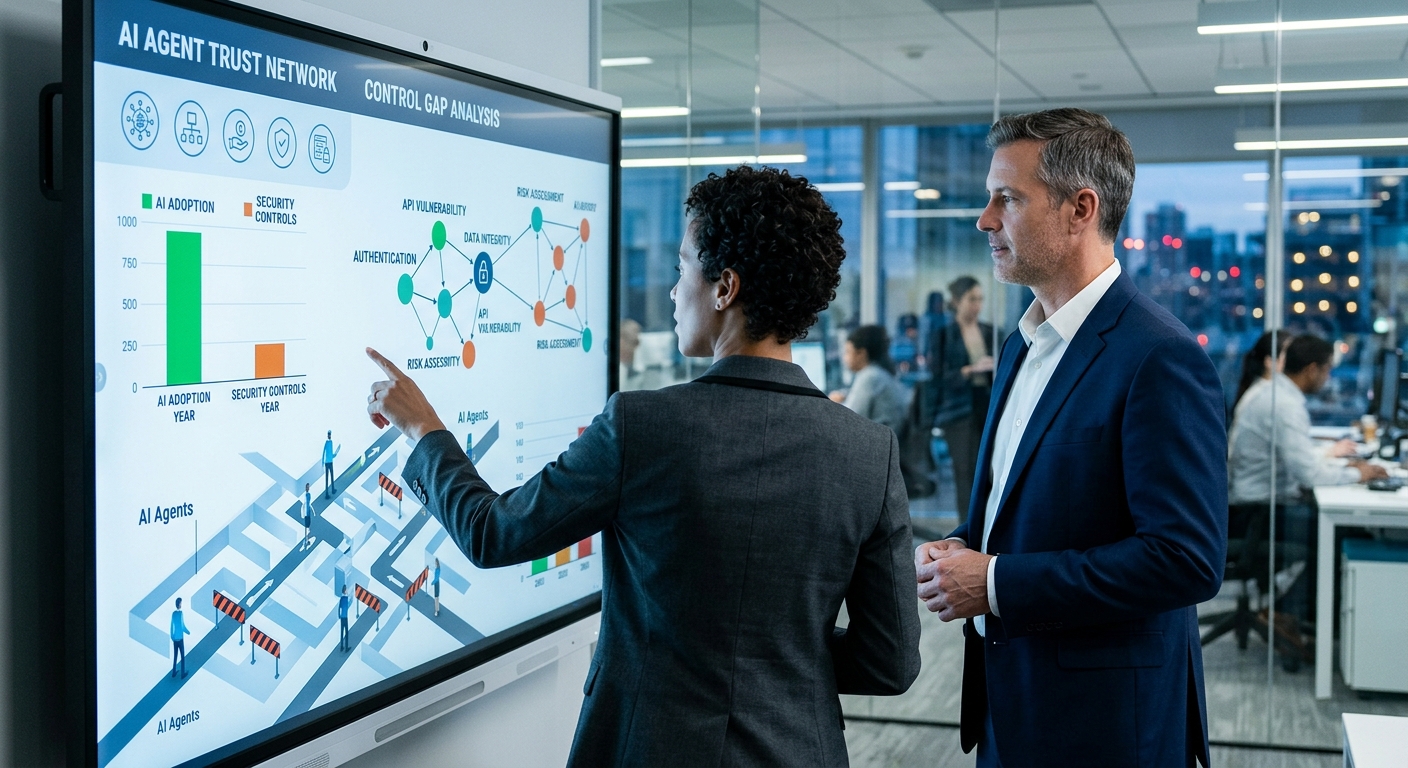
The governance gap is already apparent. In 2025, Gartner found that 75% of surveyed IT application leaders were piloting or deploying some form of AI agent, while only 15% were considering, piloting or deploying fully autonomous agents. Just 13% believed their organization had adequate governance. That distinction matters: agent activity may be proliferating even when organizations retain human oversight and have not established consistent controls for autonomous action.
Policy maturity is also lagging deployment. An EMA announcement covering a survey of 271 IT, security and IAM professionals found that 79% of organizations without written agentic-AI policies had deployed agents anyway, while 41% reported security or reliability concerns with their IAM provider. This is the operational setting for Radware, which introduced Agent Trust Management on September 29, 2026, as part of its Cloud Application Protection services.
Identity Is Necessary, but It Does Not Establish Trust
Agent identity is becoming a prerequisite for governance, not a complete security decision. Enterprises need to know which agent is requesting access, which party it represents, what credentials it uses, which tools it can invoke and which actions it is allowed to perform. OAuth 2.0 and OpenID Connect provide relevant delegated-access foundations, while identity providers such as Microsoft Entra ID, Okta and Ping Identity are extending identity and lifecycle concepts to non-human actors.
But authentication answers only part of the question. A legitimate agent may be granted excessive privileges, be manipulated through prompt injection, encounter poisoned tool output or be redirected into an unintended workflow. The more consequential the action, changing account details, accessing customer records, submitting a payment or completing a checkout, the less useful a simple allow-or-block decision becomes.
That is why trust management is emerging as a separate product category. The Bot And Agent Trust Management Software Landscape, Q4 2025 defines the category around continuous relationship assurance, malicious-automation detection and identifying AI-agent intent. Its emergence reflects a shift from asking whether traffic looks automated to asking whether an authenticated automated actor should be allowed to take a specific action at a specific point in a workflow.
From Broad Bot Decisions to Workflow-Level Permissions
According to Radware’s H1 Global Threat Analysis Report, 77% of organizations are actively deploying or implementing AI agents, yet only 17.2% report full visibility into the AI agents operating within their environments. These are sponsor-controlled findings, but independent research also indicates that visibility and containment remain weak: IDC reported in 2026 that 60% of security leaders lacked basic agent-containment controls, and 35% said they could not shut down a rogue agent after deployment.
For application-security teams, that creates a new runtime problem. Conventional bot management can identify suspicious automation and reduce fraud or abuse. Agent governance requires more contextual decisions: whether a verified agent can browse a catalog, retrieve pricing, access a loyalty account, initiate a transaction or interact with an API containing sensitive information.
The governing principle should be least privilege applied to a bounded task. An agent allowed to research a product should not automatically receive permission to log in, export customer data or complete a purchase. Equally, access should be revocable when the agent’s behavior changes or a related human authorization expires.
Radware’s Intent-Based Approach
According to the company, Radware Agent Trust Management is designed to capture an agent’s declared intent through active conversation, compare subsequent actions with that intent and apply permission-based governance to workflows. The offering uses multi-signal identification, including request headers, client-side behavioral signals and direct agent responses. It also supports identification and classification of Web Bot Auth-compliant and non-compliant agents, with cryptographic verification for standards-compliant agents, Radware says.
The company positions session-level visibility as a way to examine an agent’s identity, stated purpose, actions and navigation path. Its proposed policy model would, for example, permit browsing while restricting login or checkout functions. That is a practical distinction for retail, travel and financial-services applications, where agent traffic can move rapidly from information gathering to sensitive action.
"AI agents are fundamentally changing how applications are accessed and used. Organizations need to be able to embrace this shift while maintaining visibility and control over agent activity. Agent Trust Management enables them to establish trust and control what agents can do, so they can participate in the agent economy while protecting critical applications, business processes and data." David Aviv, chief technology officer, Radware
The key test will be whether declared intent can be translated into enforceable, auditable policies without creating brittle rules that interrupt legitimate agent-driven activity. Intent signals can add useful context, but they should not replace authentication, authorization, API protections, behavioral monitoring and human accountability for high-impact actions.
Runtime Enforcement Must Connect to Governance
The NIST AI Risk Management Framework organizes AI controls around Govern, Map, Measure and Manage. NIST’s 2026 AI-agent standards work emphasizes agent authentication, identity infrastructure, security evaluation and interoperable protocols for human-agent and multi-agent interaction, themes also examined in Agentic AI Governance: NIST Standards for Autonomous.
For practitioners, that suggests a layered operating model:
- Maintain an inventory of agents, owners, credentials, tools and permitted business processes.
- Issue distinct non-human identities and task-scoped credentials rather than reusing human accounts or broad service identities.
- Apply authorization at runtime, especially around API calls, account access, financial activity and data export.
- Log agent decisions, tool calls and policy outcomes so security and compliance teams can investigate incidents.
- Establish a rapid revocation path for agents, credentials and delegated permissions.
Model Context Protocol may simplify agent-to-tool communication, but it does not independently resolve authorization or auditability. Organizations still need controls around the protocol layer to determine which agent can call which tool, under which conditions and with what record of the interaction.
Common Questions
How is AI-agent trust management different from identity and access management?
IAM establishes who or what an agent is and can provide credentials, authentication and lifecycle controls. Trust management adds runtime assessment of what the agent is doing, whether its actions align with its stated purpose and whether it should retain access to a particular workflow.
Can an enterprise allow AI agents to browse without allowing them to transact?
Yes. Radware’s press release describes permission-based workflow governance that can allow an agent to browse while restricting actions such as login or checkout. That model reflects least-privilege access, in which permissions correspond to a bounded task rather than general application access.
What should security teams prioritize before scaling agent access?
Teams should start with agent inventory, accountable ownership, distinct identities, scoped permissions, runtime authorization, logging and revocation procedures. These foundations help address risks including excessive delegation, prompt injection, untrusted tool outputs and weak audit trails.
What Comes Next
The AI-agent economy will not be secured by one control or vendor category. As agents gain access to customer-facing applications and internal processes, enterprises will need to combine identity governance, API security, application-layer enforcement and continuous monitoring. The launch highlights an increasingly important question for security leaders: not simply whether an agent is authentic, but whether its current request remains appropriate, authorized and observable.