 ⬇️
Key Takeaways
- Human involvement in breaches is pushing cyber insurers to examine identity, access, and employee-facing controls more closely.
- MFA, endpoint protection, resilient backups, and tested recovery processes increasingly affect ransomware coverage eligibility.
- Organizations need evidence that security controls remained operational, not just affirmative answers on an insurance application.
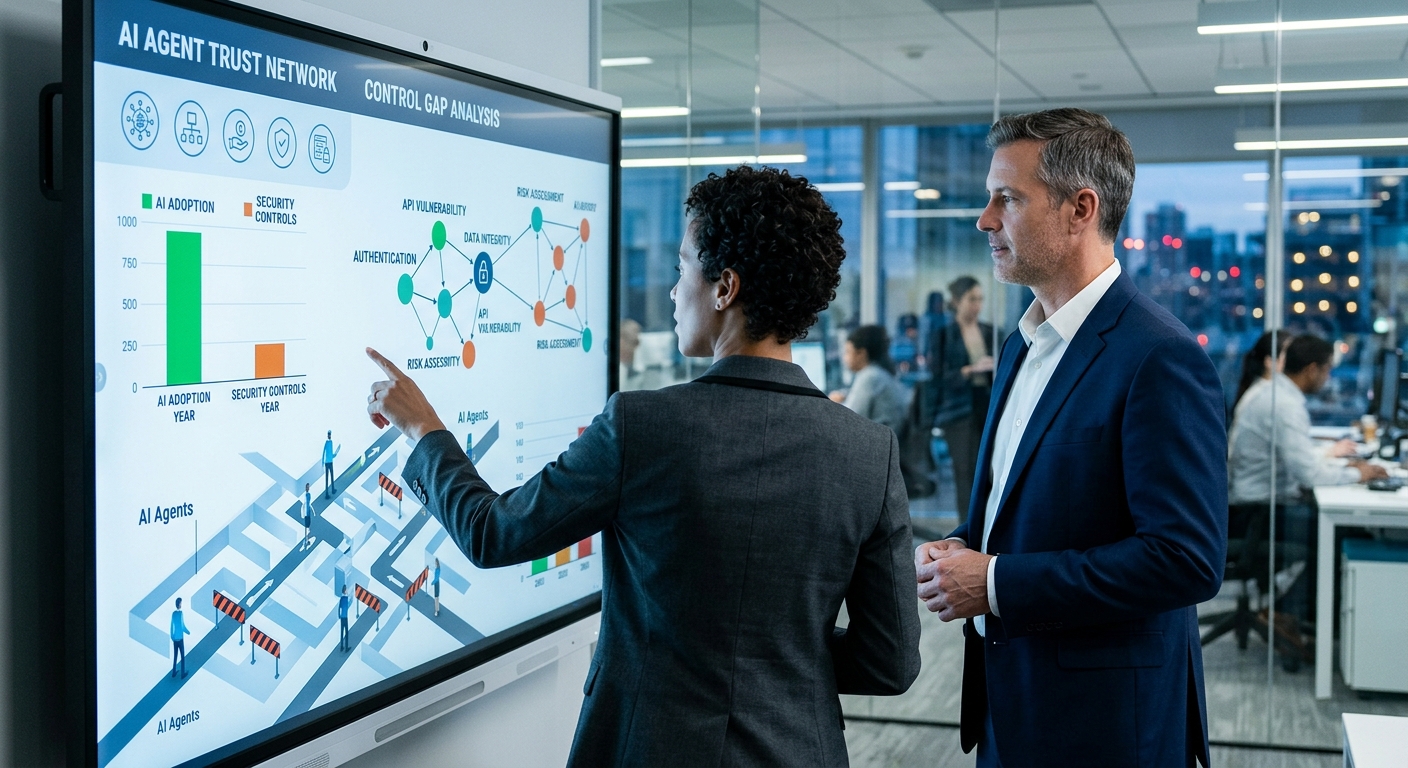
Verizon’s 2026 Data Breach Investigations Report says 62% of confirmed breaches involve a human element. For business leaders, that finding is more than another reminder to schedule security training. It helps explain why cyber-insurance underwriting has shifted toward close examination of how organizations manage identities, endpoints, privileged accounts, email, and remote access.
The central issue is verification. Insurers increasingly want to know whether a control is deployed across the full environment, whether exceptions exist, and whether the organization can prove the control was working before an incident. A checked box on an application carries less weight when coverage, exclusions, or a future claim may depend on the underlying evidence.
MFA illustrates the change. SWIF, citing Marsh data, reported that 99% of cyber-insurance applications in 2025 specifically asked about MFA. Applications also commonly addressed endpoint detection and response, privileged-access management, immutable backups, email security, and patching.
Coverage breadth matters here. MFA protecting one cloud application does not address exposed remote desktop services, administrator accounts, email, virtual private network access, or other cloud services. Underwriters may ask where MFA is enforced, which users are exempt, what authentication methods are permitted, and how administrators monitor enrollment.
Human risk cannot be treated purely as a training problem. Employees can approve deceptive prompts, reuse credentials, mishandle sensitive information, or fall for convincing social engineering. Technical controls can limit how far one mistake travels. Conditional access, phishing-resistant authentication, least-privilege policies, endpoint monitoring, and timely account removal all reduce the opportunity created by a compromised identity.
Backups are receiving similar attention. Insurers increasingly look for immutable or offline copies, separate credentials, restricted administrative access, and documented restoration tests. Help Net Security reported Coalition Incident Response guidance emphasizing the ability to rebuild identity systems, critical applications, and files on clean infrastructure.
That distinction is important. Having backup files is not the same as demonstrating recoverability. Could the business restore its directory services if ransomware damaged both production systems and connected backup infrastructure? Could it recover critical applications in the right order, within an acceptable period, without relying on credentials that attackers had already compromised?
Testing tends to expose awkward dependencies. A database may recover correctly while an authentication service does not. A clean server image may be available, but the configuration records needed to rebuild it may be outdated. These details can determine whether an interruption lasts hours, days, or longer.
Financial exposure adds urgency. Reinsurance News, reporting Aon’s 2026 findings, said the average global ransomware claim reached approximately $713,200 in 2025, up from $374,400 in 2024. That increase supports evaluating limits against realistic scenarios involving business interruption, restoration, extortion, legal advice, forensic investigation, and notification costs, rather than choosing coverage primarily by premium.
Documentation is becoming part of the control environment too. Useful underwriting and claims records can include MFA configuration exports, EDR coverage reports, patching dashboards, backup restoration results, tabletop exercise findings, and incident-response retainers. Organizations also benefit from preserving a defensible incident timeline showing when suspicious activity was detected, when access was restricted, and how recovery decisions were made.
That said, insurance remains a financial risk-transfer mechanism, not a substitute for security operations. The more immediate shift is organizational: security, legal, finance, risk, and insurance teams need a shared view of what the application promises and what the technology actually delivers.
A practical starting point is to review every renewal answer with the people responsible for operating the relevant control. Evidence should be retained, exceptions should be disclosed accurately, and recovery plans should be exercised. In a market scrutinizing both human exposure and technical resilience, demonstrable control performance can carry far more value than policy language alone.